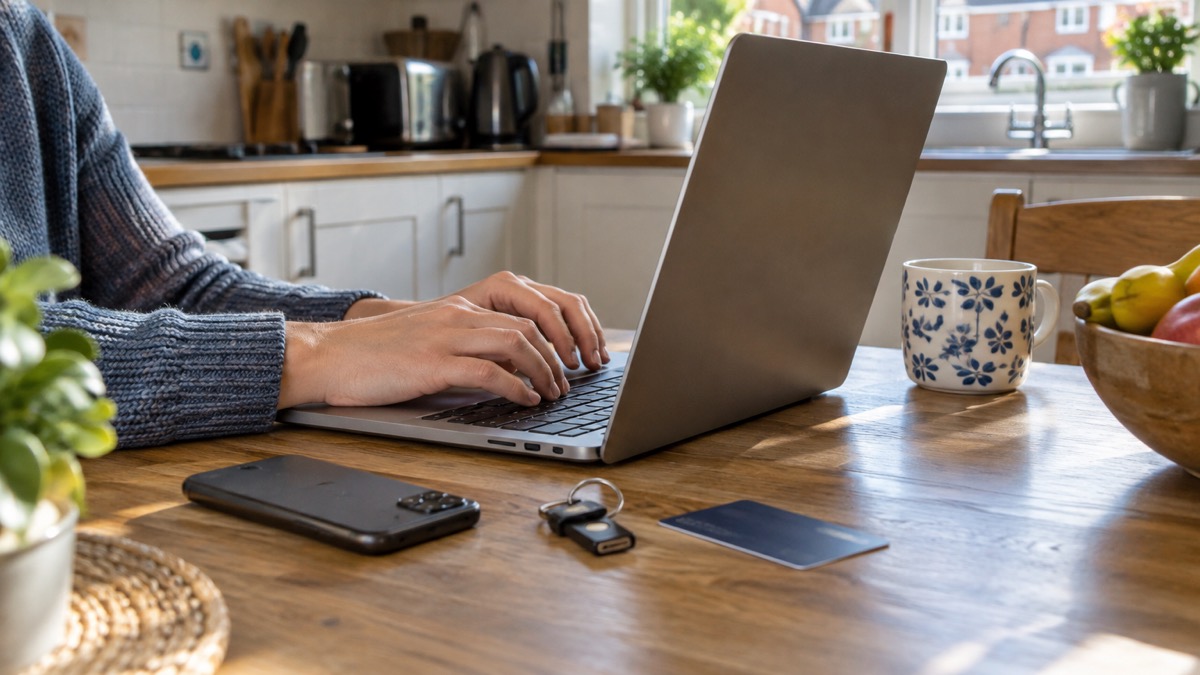
If you do four things, you will make it very hard for a criminal to take over your online life. First, protect your email account above all others, because whoever controls your email can reset the passwords on everything else. Second, give that email account a strong password that you use nowhere else, made by combining three random words. Third, turn on 2-step verification (2SV) on your email and your bank accounts, so a stolen password alone is not enough to get in. Fourth, use passkeys where they are offered, or a password manager to create and remember a different password for every service1.
This is the advice of the National Cyber Security Centre (NCSC), the UK's official cyber security body, and it is deliberately simple. You do not need technical knowledge, and none of it costs money. The NCSC's current password guidance now recommends making passkeys your first choice of login wherever they are offered2. This page sets out the whole approach in the order you should act on it, with links to step-by-step guides for each part.
Why your email account comes first
Your email account is the master key to your online life. The NCSC is blunt about what happens if a criminal gets into it: they could use it to access all your other accounts, access information about you including banking and social media details, and send emails and messages pretending to be from you1. Wiltshire and Swindon's local resilience forum puts the same point another way: criminals can use your email to access many of your personal accounts, leaving you vulnerable to identity theft6.
The reason is password resets. When you forget a password for your bank, your shopping accounts or your social media, the recovery link goes to your email inbox. A criminal sitting in that inbox does not need to know any of your other passwords: they can request a reset on each service in turn and click the links themselves. The NCSC's guidance on email passwords lists exactly this among the risks, alongside accessing private information about you including your banking details, and posting emails and messages pretending to be from you7.
There is a second reason, and it is about password reuse. If you have used the same password across different accounts, cyber criminals only need one password to access all your accounts7. The NCSC's password manager guidance explains the mechanics: if one of your accounts is compromised, a hacker can try the same password on your other accounts and potentially gain access to them too2. So a breach at a shop you barely use becomes a breach of your email, and through your email, of everything.
One specific trick is worth knowing about even before anything goes wrong. Cyber criminals are known to set up a forwarding rule in a hacked email account, so they automatically receive a copy of every email sent to it, which could allow them to reset your passwords even after you take the account back8. If you ever recover a hacked email account, checking for these rules is one of the NCSC's recovery steps, and we cover it in how to check for forwarding rules set by hackers.
A strong and separate password for your email
Start with the email password itself. The NCSC's top tips are specific: your email password should be strong and different from all your other passwords, and you should combine three random words to create it3. The example the NCSC gives in its community risk guidance is "BallDogRed": three unrelated words, strung together, long enough and strong enough to resist guessing but still memorable to you9.
Three random words works because length and unpredictability matter more than swapping letters for symbols in a word you will then forget. The NCSC's dedicated guidance on the technique, reviewed in December 2021, notes that you can add numbers and symbols if the service requires them, or use a password manager, which can create strong passwords for you and remember them10. For the email password itself, the one you must be able to type without help, three random words is the practical answer.
The "separate" part is just as important as the "strong" part. Local resilience forums across England repeat the NCSC's basic steps for individuals and households: use a strong and separate password for your email, install the latest software and app updates, turn on 2-step verification, use password managers to store passwords safely, and back up your data11. Essex's community preparedness site adds the underlying habits: use strong passwords and be vigilant to phishing emails, text messages and phone calls, and keep all software and systems up to date, including mobile phones12.
If you want a fuller walk-through of creating a password you can actually remember, see how to create a strong password you can remember. If you suspect your email has already been compromised, the NCSC suggests checking whether your address has appeared in a known data breach, which we cover in how to check if your email was in a breach.
Turn on 2-Step Verification for email and banking
A strong password is not the whole answer, because passwords can be phished out of you by a convincing fake email or website. That is why the NCSC calls turning on 2SV "the first, and most important, step" to protect you if your password gets phished or otherwise compromised2. Wiltshire and Swindon's guidance spells out what it buys you: 2SV on your email account will prevent a criminal from accessing it even if they know your password6.
How it works is simple. 2SV, also known as two-factor authentication or 2FA, usually works by sending you a PIN or code, often via SMS or email, to prove it is really you8. The NCSC's poster for the public describes the effect: "2SV gives you twice the protection by adding a second step when you log on, so even if cyber criminals have your password, they can't access your account"3. A criminal needs both your password and your phone, or your password and your second factor of whatever kind, and that combination is far harder to steal.
"2SV gives you twice the protection by adding a second step when you log on, so even if cyber criminals have your password, they can't access your account"
Where to switch it on: if 2SV is available for an account, the option is usually found in the security settings for that account3. The NCSC also publishes how-to guides for popular services at ncsc.gov.uk/2sv, and suggests looking in the security settings included in antivirus or password manager tools1. Our step-by-step guide is at how to turn on 2-step verification, and if you do not have a mobile phone, see can you set up 2-step verification without a mobile?.
Which accounts matter most? The NCSC's recovering-a-hacked-account guidance is clear: it is worth taking the time to set up 2SV on important accounts like email and banking, even if these are already protected by a strong password, and it only takes a few minutes4. Our checklist at which accounts to protect with 2-step verification works through the list. One point that is easy to miss: your cloud accounts need the same treatment, because anyone who can access your cloud account also has access to the backups stored in it13. If you keep copies of important files in the cloud as part of your household preparedness, protect that account with a strong password and 2SV as well.
A note on codes by text message: receiving a code by SMS is the most common form of 2SV and it is far better than nothing. Where a service offers a stronger second step, such as an app on your phone or a passkey, choose that instead, but do not delay switching 2SV on while you decide.
Passkeys: the NCSC's first choice of login
The NCSC's password guidance now puts this in plain terms: "The NCSC recommends making passkeys your first choice of login and using them wherever they are offered"2.
A passkey replaces the password entirely. Instead of typing something a criminal could phish, guess or reuse, you prove who you are with something bound to your device, such as a fingerprint or face check, and the service verifies a cryptographic key. Because there is no password to type into a fake website, the classic phishing trick of steering you to a lookalike login page has nothing to steal. We explain how they work and whether they suit your household in what is a passkey and should you use one?.
The practical instruction is straightforward. Wherever a service you use, your email provider, your bank, your social media accounts, offers passkeys, set one up and prefer it at login2. For accounts that do not yet offer passkeys, the NCSC's advice is to continue using a strong and unique password and two-step verification2. Passkeys are not an extra layer on top of a password; they are a replacement for it, so the two approaches cover different accounts.
If you have already given out a password, for example by typing it into a phishing site, the NCSC's phishing guidance adds a useful option: change the passwords on any of your accounts which use the same password, and if available, you could use a passkey instead14. That closes the door behind you. If you entered banking or card details as well, contact your bank straight away, and if you use online banking, cancel the card there15.
Password managers: a different password for every account
The weakness most households have is not one weak password but one reused password. A password manager fixes that at the source. As the NCSC puts it, a password manager stores passwords safely for you, meaning you can have unique passwords for each service without needing to remember them2. Wiltshire and Swindon's guidance says the NCSC encourages people to use password managers, which can create strong passwords for you and remember them6, and Essex Prepared makes the same point: using a password manager can help you create and remember passwords12.
You keep one strong password, or a passkey, to unlock the manager, and it does the rest: generating long random passwords for every service and filling them in when you need them. That removes the temptation to reuse, which is the single habit that turns one breach into many. Our guide at do you need a password manager? weighs up whether one suits your household.
Two related questions come up constantly, and the NCSC answers both directly.
Saving passwords in your browser. It is safe to save passwords in your browser on your own devices, and it is the easiest way to remember them2. The browser's built-in manager is, in effect, a simple password manager. The condition is that those passwords are only as secure as your devices and accounts, so the NCSC's warning is not to switch off the security auto-update feature for your browser and operating system2. Keep updates on, and keep a screen lock on the device itself. More detail is at is it safe to let your browser save passwords?.
Writing passwords down on paper. This can be done safely, because an attacker would need physical access to where the passwords are stored2. It can suit people who need regular support to manage their online affairs, for example from family or carers. Three cautions from the NCSC: make sure the written passwords are not predictable or guessable, consider who has access to where they are kept, and check you are not breaking the service's terms and conditions, because some online banking services forbid writing down passwords2. See is it safe to write your passwords down?.
| Way of storing passwords | What it does | Who it suits | The condition |
|---|---|---|---|
| Password manager | Creates and remembers a unique password for every service | Anyone with several accounts | Protect the manager itself with a strong password or passkey2 |
| Browser's saved passwords | Fills in passwords on your own devices | Most households | Only as secure as your devices: keep updates and screen locks on2 |
| Written on paper | No digital copy to steal | People who need regular support, or who cannot use a manager | An attacker needs physical access; check banking terms2 |
| Memory, three random words | Nothing to lose or lock | The email password, which you must always be able to type | Must be different from every other password3 |
Smart devices and the UK security law
Account security does not stop at your email and your bank. Many households now have devices that connect to the internet or the home network, and each one is a door. The UK's security law for smart devices, in force from 29 April 2024, covers consumer smart devices that connect to the internet or your home network: smart speakers, smart TVs and streaming devices, smart doorbells, baby monitors and security cameras, cellular tablets, smartphones and game consoles, wearable fitness trackers including smart watches, and smart domestic appliances such as light bulbs, kettles, thermostats, fridges and washing machines16.
The law means manufacturers must not supply devices that use default passwords, which can be easily discovered online and shared, and they must provide a point of contact for reporting security issues which, if ignored, could make devices exploitable by cyber criminals16. The NCSC's guidance on smart devices in the home confirms the same requirements from 29 April 2024, including a stated support end date so you know how long the device will receive security updates17.
The law helps, but it does not replace your own action. If a default password is used, a criminal could log into a smart device and use it to access a local network, or conduct cyber attacks16. So when you set up any new device, change any default password immediately, and create a secure one, for example by combining three random words16. Electrical Safety First, which advises on smart home safety independently, adds the general rule for smart home devices: a strong password should have plenty of characters and be a mix of numbers, symbols, capital and lower-case letters18. Our page on smart speakers, cameras and baby monitors covers the set-up steps in full.
Where to get help if an account is taken over
Know the signs before you need them. You may have been hacked if you can no longer access your accounts, or if there is activity you do not recognise, such as changes to security settings or password reset messages you did not request19. Messages sent from your account that you do not recognise, or contacts telling you they received something odd from you, are the same signal.
The first step is to go to the account provider's website and search their help or support pages to find the account recovery process4. The NCSC's recovery guidance then works through the steps, and two matter especially for email: check there are no unwanted forwarding rules in your email account, because criminals may have set one up to receive copies of all your emails8, and set up 2-step verification once you have control back, so the same attacker cannot simply walk in again8. Our full walkthrough is at what to do if an online account is hacked, with a narrower guide for email at how to recover a hacked email account.
Tell the people who matter. Notify contacts, friends or followers that you were hacked, and suggest they treat any recent messages sent from your account with suspicion4. If the account cannot be recovered with the online service, the NCSC's advice is to create a new account, give your contacts the new details, tell them you have abandoned the old account, and update any bank, utility or shopping websites with your new details8.
The NCSC also suggests reading its guidance about recovering a hacked account in advance, so you know what to do if you experience an incident19. That is good preparedness practice: the middle of an incident is the worst time to be searching for instructions. If you entered banking or card details to the criminal, contact your bank straight away and cancel the card through online banking15, and see gave your bank details to a scammer: what now.
Reporting helps others, not just you. Forward suspicious emails to the NCSC's Suspicious Email Reporting Service at report@phishing.gov.uk5. The NCSC will analyse the suspect email and any websites it links to, and may work with hosting companies to remove links to malicious websites and raise awareness of commonly reported suspicious emails via partners20. Our guide at how to report a phishing email covers the details.
Scam emails that quote your password
One scam deserves special mention because it frightens people into paying. A sextortion scam is when a criminal attempts to blackmail someone, usually by email, claiming they have login details or a video of the victim visiting an adult website, and threatening to disclose this unless the victim pays a ransom5. It is an example of a phishing attack, where victims receive emails that try to trick them into doing the wrong thing5.
The scale is the tell. Criminals will send millions of emails in the hope that someone will pay5. If the message includes one of your passwords, do not worry: it is probably from an old breach of personal data. But change that account password immediately, and anywhere else you use the same password21. The NCSC's advice is not to engage with the criminal: forward the email to report@phishing.gov.uk, the Suspicious Email Reporting Service, and then delete it5. You can also check whether your account has been compromised and get future notifications at haveibeenpwned.com22. Our page sextortion emails that quote your password goes through it step by step.
The same hygiene protects you here as everywhere else: a unique password per service means an old breach reveals nothing useful, and 2SV means an old password opens nothing. For the wider picture of scam messages that follow data breaches, see how to spot scam messages after a data breach.
The habits that hold it all together
Everything on this page rests on a few habits that the NCSC and local resilience forums repeat consistently. Use a strong and separate password for your email. Turn on 2-step verification on email and banking. Use passkeys where offered, and a password manager for everything else. Install the latest software and app updates, including on your mobile phone11. Back up your data, and protect the cloud account holding those backups with a strong password and 2SV13. Be vigilant to phishing emails, text messages and phone calls12, and review your privacy settings, thinking about what information you post and publish online, because easily viewed personal information makes criminals' phishing emails more convincing12.
You can reduce the likelihood of being phished by thinking about what personal information you and others post about you, and by reviewing the privacy settings within your social media accounts23. That applies to family members too: a child's public profile can tell a criminal enough about the household to make a fake message convincing.
For the whole picture of how a major cyber incident could affect your household, from bank systems going down to NHS appointments, see our guide to cyber attacks and major IT failures. If you want a single page to work through with the family, start with the home online security checklist.
Sources (23)
- Using passwords to protect your devices and data (infographic), National Cyber Security Centre, 2026
- Password managers: top tips for staying secure online, National Cyber Security Centre, reviewed 21 May 2026
- Top tips for staying secure online (poster), National Cyber Security Centre, 2024
- Recovering a hacked account, National Cyber Security Centre, 24 August 2022
- Sextortion scams (infographic), National Cyber Security Centre, 2026
- Having a strong password, Wiltshire and Swindon Prepared, 2026
- Use a strong and separate password for your email, National Cyber Security Centre, reviewed 21 December 2021
- Recovering hacked accounts (infographic), National Cyber Security Centre, 2026
- Community Risk Register, West Yorkshire Prepared, 2025
- Three random words, National Cyber Security Centre, 21 December 2021
- Cyber crime, Wiltshire and Swindon Prepared, 31 May 2024
- Cyber security: protecting your family, Essex Prepared, 2026
- Always back up your most important data, National Cyber Security Centre, 17 December 2018
- What to do: phishing scams, National Cyber Security Centre, 5 September 2022
- Phishing: respond and recover, National Cyber Security Centre, 2026
- New security law for smart devices, National Cyber Security Centre, 2024
- Smart devices: using them safely in your home, National Cyber Security Centre, 29 April 2024
- Smart homes safety advice, Electrical Safety First, 2026
- Recovering a hacked account or service, National Cyber Security Centre, 11 January 2024
- Report a scam email, National Cyber Security Centre, 26 November 2021
- Sextortion emails: respond and recover, National Cyber Security Centre, 2026
- Sextortion scams: how to protect yourself, National Cyber Security Centre, 1 November 2018
- Suspicious email actions, National Cyber Security Centre, 26 November 2021
 Accounts to Protect With 2-Step
 After Fixing an Infected Device
 Home Online Security Checklist
 Antivirus Software
 Backing Up Files and Photos
 Council Online Services Down
 Your Details in a Data Breach
 FluBot Fake Parcel Texts
 Hacked Online Accounts
 How Services Respond
 Malware Signs and Removal
 National Cyber Security Centre
 NHS Services During an IT Outage
 Keeping Key Records Offline
 Shopping Online Safely